Adopt AI fast. Without the exposure.
Fractional CAIO and AI security architecture for regulated enterprises
Agents are the new identity in your enterprise. Most have not been secured yet.
Security primitives, AI safety, and layered protection that survives the audit.
Security architecture first. Adoption follows.
Controls go in before the first agent ships. Agent identity, pipeline security, and AI safety are designed as one system, with AI observability watching it in production, so nothing gets bolted on after the audit finds it.
A framework built and run at cloud scale, mapped to NIST AI RMF, ISO 42001, and the EU AI Act, and hardened against the OWASP Top 10 for LLM applications. Your teams ship faster because the controls are already there.
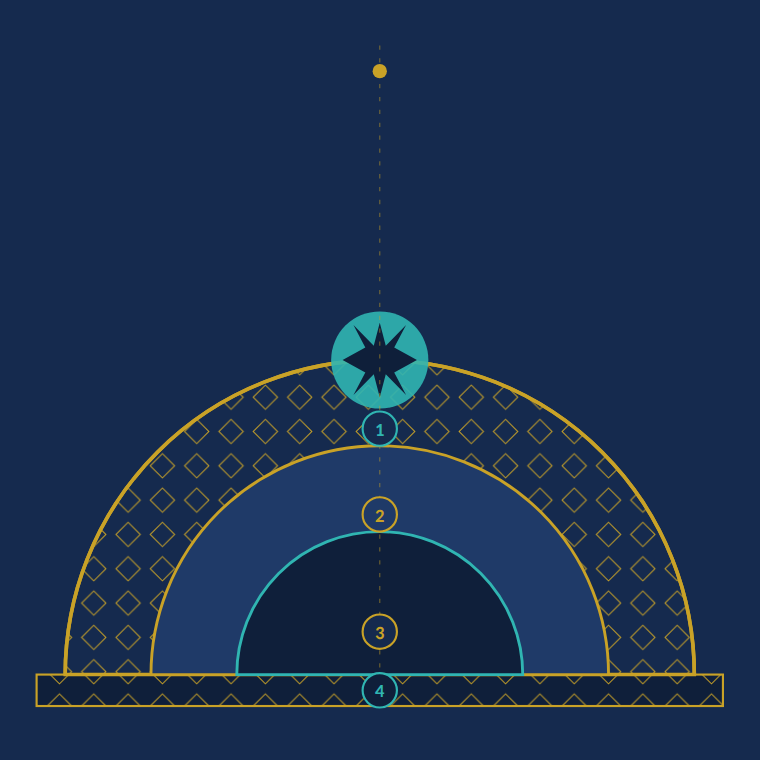
Layered protection, built like a dome
Most AI security is a stack of controls piled up, each one hoping the next will catch what it missed. This is a dome. Agent identity at the core, pipeline security in the shell, runtime detection on the surface, AI safety in the foundation. Every layer bears on the others. Crack one, and the rest still hold.
4
Layers of protection
Identity, pipeline, safety, observability. Four layers set like tiles in a dome. One system, no single point of failure.
3
Frameworks mapped
NIST AI RMF, ISO 42001, EU AI Act. Controls mapped once, evidence generated as you build. Evidence that exists because the system ran, not because someone went looking for it.
6
Ways to engage
From a fractional CAIO seat to a single board briefing. Architecture, governance, safety, due diligence. Start where the risk is. Scale when the board asks for more.
Six ways to engage
Every engagement starts from one question.
What would it take for your board, your regulator, and your security team to say yes to this AI investment?
Fractional Chief AI Officer
An executive-level AI leader on a fractional basis. Sets AI strategy, owns the upside and the risk posture, and sits with your CIO, CTO, CISO, and board without the cost of a full-time hire. Decisions made at the speed the business needs, with the accountability a regulator expects.
AI Security Architecture
AI security is an architecture decision, not a product purchase. Agents are a new class of identity, and most enterprises have not yet secured them. Authorization decided at the moment an agent acts, pipelines hardened from IDE to production, and threat models built on OWASP and MITRE ATLAS. Architecture that fails safe.
AI Safety and Responsible AI
Most safety programs report on yesterday. The Safety Health Index reports now. One continuously computed score of your AI estate's safety posture across five indicators. Agent boundary controls, identity integrity, content safety, tool safety, and operational health, each an independent detection surface, with the evidence written as it runs.
Governance, diligence, and the boardroom
Governance that produces evidence as a byproduct of building, diligence that prices AI risk before the deal closes, and briefings that leave the board with a decision to make, not a subject to study.
AI Governance and Compliance Readiness
The EU AI Act's high-risk obligations are now live, and most control programs still run on screenshots and spreadsheets. A Responsible AI control program mapped once to NIST AI RMF, ISO 42001, and the EU AI Act, with evidence generated as you build. Nothing reconstructed the week before the audit.
AI Due Diligence for Private Equity
Every target now claims to be an AI company. Few can show what the models do, where the agents reach, or whether the data they trained on was theirs to use. Technical and governance diligence before you sign, pricing AI risk into the deal, and a 100-day plan for the exposure you inherit.
Executive and Board AI Briefings
Agents now act with real privileges, regulators are asking directors by name what they knew, and most boards are still briefed in vendor slides. Sessions in plain language on AI risk, regulation, and opportunity, framed in financial and operational terms. The board leaves knowing what to decide, and what it will cost to wait.
Ready to adopt AI without the exposure?
Thirty minutes on your AI estate as it actually is. The upside nobody has sized, the exposure nobody has owned, and the one move that gets you both. The frameworks come later. The judgment comes first.
Let's talk
Telephone: +1 617 335 5500
E-mail: info@mozhie.ai
Address: Cambridge, MA